



Excellence Begins Here
ISO 27002 Lead Implementer Certification Overview
The ISO 27002 Lead Implementer Certification validates a candidate's ability to design and implement information security control frameworks based on ISO/IEC 27002 guidance. The examination assesses advanced knowledge of security governance structures, risk management practices, control implementation strategies, and monitoring mechanisms used to protect organizational information assets.
It evaluates competence in conducting security gap analysis, establishing security policies, integrating operational controls, and monitoring the effectiveness of implemented safeguards. Successful candidates demonstrate the capability to lead security control implementation initiatives and ensure structured, compliant, and sustainable information protection practices.

Skills You Will Gain
Security Gap Analysis
Ability to evaluate existing information security practices against ISO 27002 guidance and identify implementation gaps. This supports structured improvement planning.
Implementation Planning
Ability to develop comprehensive security control implementation roadmaps including responsibilities, timelines, and governance oversight. This ensures controlled deployment of security practices.
Process Alignment
Ability to integrate ISO 27002 control domains into operational workflows and governance structures. This strengthens consistency in information security management.
Security Documentation Framework
Ability to establish and maintain structured security policies, procedures, and control documentation. This supports traceability and compliance.
Security Performance Monitoring
Ability to define monitoring mechanisms that evaluate the effectiveness of implemented security controls. This enables proactive security oversight.
Continual Improvement Leadership
Ability to initiate and manage improvement initiatives that enhance information security resilience and operational protection. This supports sustainable security management practices.
Exam

Multiple Choice
30 Questions
40 Minutes
Closed Book
 Minimum required score to pass: 60%
Key Exam Highlights
- Standardized Assessment
- Competency-Based Evaluation
- Secure Digital Examination Platform
- International Recognition
Why This Certification Matters?
- Lead Security Control Implementation
Plan and manage the structured deployment of information security controls aligned with ISO 27002 guidance. This strengthens organizational protection of information assets. - Strengthen Security Governance
Align operational security practices with structured governance and compliance frameworks. This improves accountability and oversight. - Enhance Process Integration
Integrate security control practices into operational and technology environments. This increases resilience against emerging security risks. - Drive Continuous Security Improvement
Establish monitoring and review mechanisms that support ongoing enhancement of information security practices. This strengthens long-term organizational security posture.
Qualify for In-Demand Jobs
- Information Security Implementation Manager
- Cybersecurity Program Manager
- Information Security Governance Manager
- Security Architecture Manager
- Information Security Operations Manager
- Cybersecurity Risk Manager
- Information Security Compliance Manager
Certification Roadmap
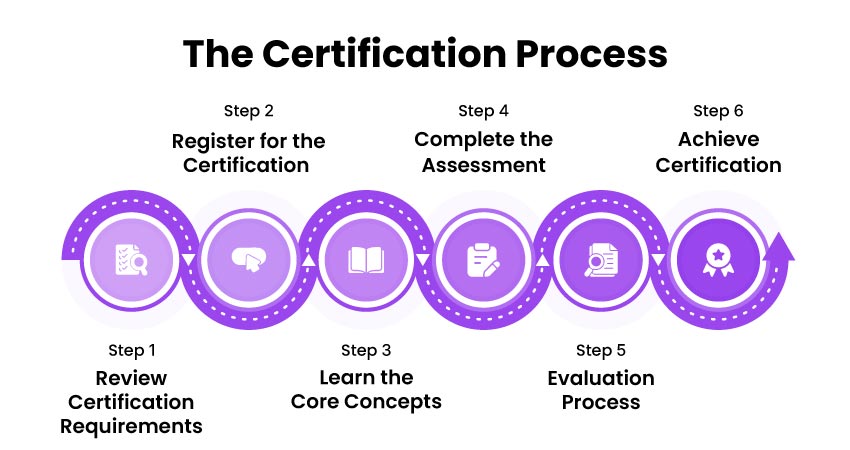
Step Forward with Globally Recognized Certification
Career Growth
Certified professionals report faster career advancement and higher recognition within their organizations after earning their certification. Many experience salary growth, expanded responsibilities.

Boost Your Career & Income

Increase your earning potential with globally valued certification.

Global Certification Board make 20% higher salaries worldwide
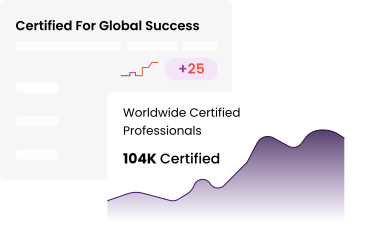
Globally Certified Professionals Over Time
Our certification program continues to grow worldwide as more learners upgrade their skills with globally recognized expertise. Certified individuals demonstrate improved .
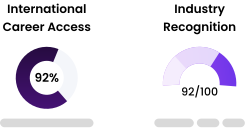
Global Opportunities
Certified professionals gain access to international job roles, cross-border work experience, and leadership positions in top organizations. and leadership positions in top organizations.

Build a Future-Ready Global Certification Career for 2026 — Backed by an Internationally Recognized Diploma
Accredited Certification issued by Global Certification Council
Frequently Asked Questions
ISO 27002 Lead Implementer Certification validates advanced knowledge of implementing information security controls based on ISO 27002 guidelines. It confirms the ability to establish and manage structured security practices within an organization. The certification reflects competence in strengthening information protection frameworks.
Information security implementation expertise is highly valued as organizations prioritize data protection and cyber resilience. This certification demonstrates the ability to design and manage effective security control frameworks. It can support career growth in cybersecurity, risk management, and compliance leadership roles.
Yes, ISO 27002 is widely recognized as an international guideline for information security controls. Organizations around the world use it to strengthen their cybersecurity practices. Because of this, the certification holds strong global relevance.
ISO 27002 is used across sectors such as finance, healthcare, government, technology, telecommunications, and retail. Organizations that handle sensitive information rely on structured security control frameworks. The certification is relevant across both private and public sectors.
The certification validates knowledge of information security controls, risk management practices, and governance frameworks. It confirms the ability to design, implement, and maintain effective security controls. It also demonstrates competence in protecting confidentiality, integrity, and availability of information.
Lead Implementer Certification focuses on establishing and managing information security controls. Lead Auditor Certification focuses on evaluating compliance and effectiveness through structured audits. The two credentials represent complementary areas of expertise.
The certification can support roles such as Information Security Manager, Cybersecurity Consultant, Security Governance Lead, or Compliance Manager. It demonstrates the ability to guide organizations in implementing strong information security controls. Many employers value certified professionals for protecting critical information assets.
Yes, the certification emphasizes real-world application of information security controls. It supports understanding of security policies, operational controls, and risk mitigation practices. This practical focus strengthens implementation capability.
Certified professionals help organizations establish structured security control frameworks. Effective implementation reduces vulnerabilities and strengthens risk management practices. This contributes to stronger protection of information assets.
Yes, Lead Implementer certification demonstrates advanced expertise in information security governance and control implementation. It strengthens professional credibility in cybersecurity leadership roles. The credential can support progression into senior security or risk management positions.
Related Certifications
ISO 27002 Foundation Certification
ISO 27002 Lead Auditor Certification
ISO 27002 Internal Auditor Certification


