



Explore All Certifications
ISO 27001 Foundation Certification
Build foundational expertise in information security management with the ISO 27001 Foundation Certification, designed to validate understanding of structured Information Security Management Systems. This certification confirms the ability to interpre...
ISO 27001 Internal Auditor Certification
Develop structured expertise in auditing Information Security Management System (ISMS) with the ISO 27001 Internal Auditor Certification designed to validate competence in conducting internal audits of security controls and risk management practices....
ISO 27001 Lead Implementer Certification
Develop advanced capability in establishing and managing Information Security Management Systems with the ISO 27001 Lead Implementer Certification, designed to validate professional competence in implementing structured information security framework...
ISO 27001 Lead Auditor Certification
Develop advanced auditing expertise in information security management systems with the ISO 27001 Lead Auditor Certification. This certification confirms the ability to plan, conduct, and lead structured audits that assess organizational information...
GCB’s Commitment to Professional Excellence
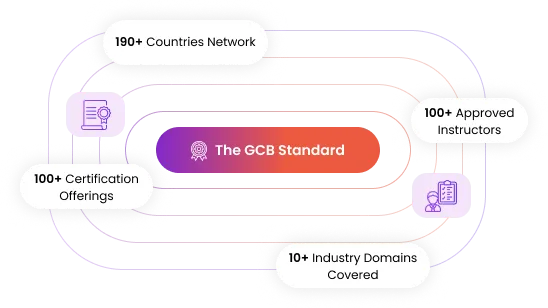
At GCB, we believe professional excellence is defined by clarity, credibility, and recognized expertise. We support individuals and organizations in demonstrating recognized expertise within their respective fields by offering certifications that deliver meaningful value across the global professional landscape. For those ready to stand apart, GCB bridges the gap between the ordinary and the exceptional through credible, globally respected recognition.
Introduction to ISO 27001 Certifications
- Topic Introduction
- Overview
Established for Lasting Success

Global Recognition
Structured to support recognition across international professional environments.

Cross-Industry Applicability
Designed to remain relevant across multiple industries and professional contexts.

Quality-Assured Standards
Maintained through structured oversight and consistent assessment principles.
Global Certification Board Validates Professional Expertise, Supporting Sustainable Careers And Enduring Success.
Frequently Asked Questions
ISO 27001 is an internationally recognized standard for Information Security Management Systems (ISMS). It provides a structured framework that helps organizations identify security risks, implement appropriate controls, and protect sensitive information. The standard also promotes continual improvement in information security practices.
ISO 27001 Certification is suitable for professionals involved in information security, cybersecurity, risk management, or IT governance. It is also beneficial for individuals responsible for protecting organizational data and managing security risks. Anyone interested in understanding information security management practices can benefit from this Certification.
Most foundation-level ISO 27001 Certifications do not require prior experience. They introduce the core concepts of Information Security Management Systems in a clear and structured way. This makes the Certification suitable for both beginners and experienced professionals.
You will learn the key principles of information security management and how organizations implement processes to protect information assets. The Certification also develops your understanding of risk assessment, security controls, and governance practices. These skills help support strong cybersecurity and regulatory compliance.
ISO 27001 Certification strengthens your understanding of internationally recognized information security practices. It can enhance your credibility in roles related to cybersecurity, IT governance, and risk management. Many organizations value professionals who understand information security standards.
Yes, ISO 27001 is widely recognized and adopted by organizations across the world. Businesses use the standard to demonstrate their commitment to protecting information and maintaining strong security practices. This global recognition makes the certification valuable for professionals.
The duration of ISO 27001 Certification depends on the certification level and learning format. Foundation-level certifications typically focus on core concepts and are shorter in duration. Advanced certifications may take longer as they cover implementation and auditing practices.
ISO 27001 is used across industries such as finance, healthcare, technology, telecommunications, and government. The standard supports organizations that need to protect sensitive information and manage cybersecurity risks. Its focus on information security management makes it relevant across sectors.

Driving Global Workforce Development with GCB
We are dedicated to global workforce development by enabling consistent professional recognition that strengthens workforce readiness across industries and regions. GCB achieves this by aligning certification scope with evolving professional requirements and internationally recognized standards.

5K+
Certifications issued globally, reflecting trusted professional recognition across diverse industries and international markets.

95%
GCB Certifications are designed for recognition across both public and private sector environments.

80%
Certification outcomes are applicable across more than one professional domain or industry.

700+
Skills Validated across recognized competency areas aligned with professional standards.

500+
Professional Roles Supported through role-aligned certification scope and assessment.

100%
Defined International Guidelines applied across all certifications to ensure consistency, credibility, and global applicability.

100+
Professional Specializations reflecting focused areas of professional practice and expertise.


